Govern every
AI agent
across your enterprise
Privify FORGE — Federated Oversight & Risk Governance Engine
Privify discovers every AI agent running in your environment — sanctioned or shadow — maps every interaction, and enforces policy in real time. Three pillars: Discovery, Observability, Governance.
You cannot govern
what you cannot see.
Every AI policy names a handful of approved tools. The first Privify FORGE scan usually finds an order of magnitude more already running — including agents nobody registered, and models that never leave the laptop.
Representative first-scan result, from the Privify FORGE demo environment.
Three pillars. One control plane.
Privify is not a single tool. It is an integrated governance layer operating at every point where AI agents exist in your enterprise.
Discovery
Find every agent — sanctioned or shadow, cloud or local. Four parallel probes across endpoints, network traffic, filesystem, and behavior patterns.
- Endpoint probe: detects AI library imports & local LLMs (Ollama, LM Studio, vLLM)
- Network probe: maps outbound calls to 116 AI providers
- File probe: finds prompt artifacts, API keys, agent configs
- MCP server auto-discovery with security assessment
- Participant registry: humans, agents, tools, APIs
Observability
See what agents do — not just that they ran. Full interaction graph across human↔agent, agent↔agent, and agent↔tool. The delegation chain made visible.
- Live interaction graph: every delegation, message, and tool call
- Trace DAG with animated replay
- Quality scoring: 6-dimension radar per agent
- Anomaly detection with baseline deviation alerts
- OpenTelemetry OTLP receiver — no rip-and-replace
Governance
Stop bad things before they complete. Policy evaluation on every interaction, mid-flight intervention, human approval gates, and quality SLAs.
- Policy engine: condition DSL, simulation mode, versioned rules
- Configurable DLP engine: SSN, PHI, API keys, and more
- AI firewall: configurable threat signatures including prompt injection & jailbreak
- Human-in-the-loop: pause any interaction for approval
Your entire AI fleet. One screen.
11 real-time panels powered by WebSocket and SSE streams. Every agent, every interaction, every policy match — visible the moment it happens.
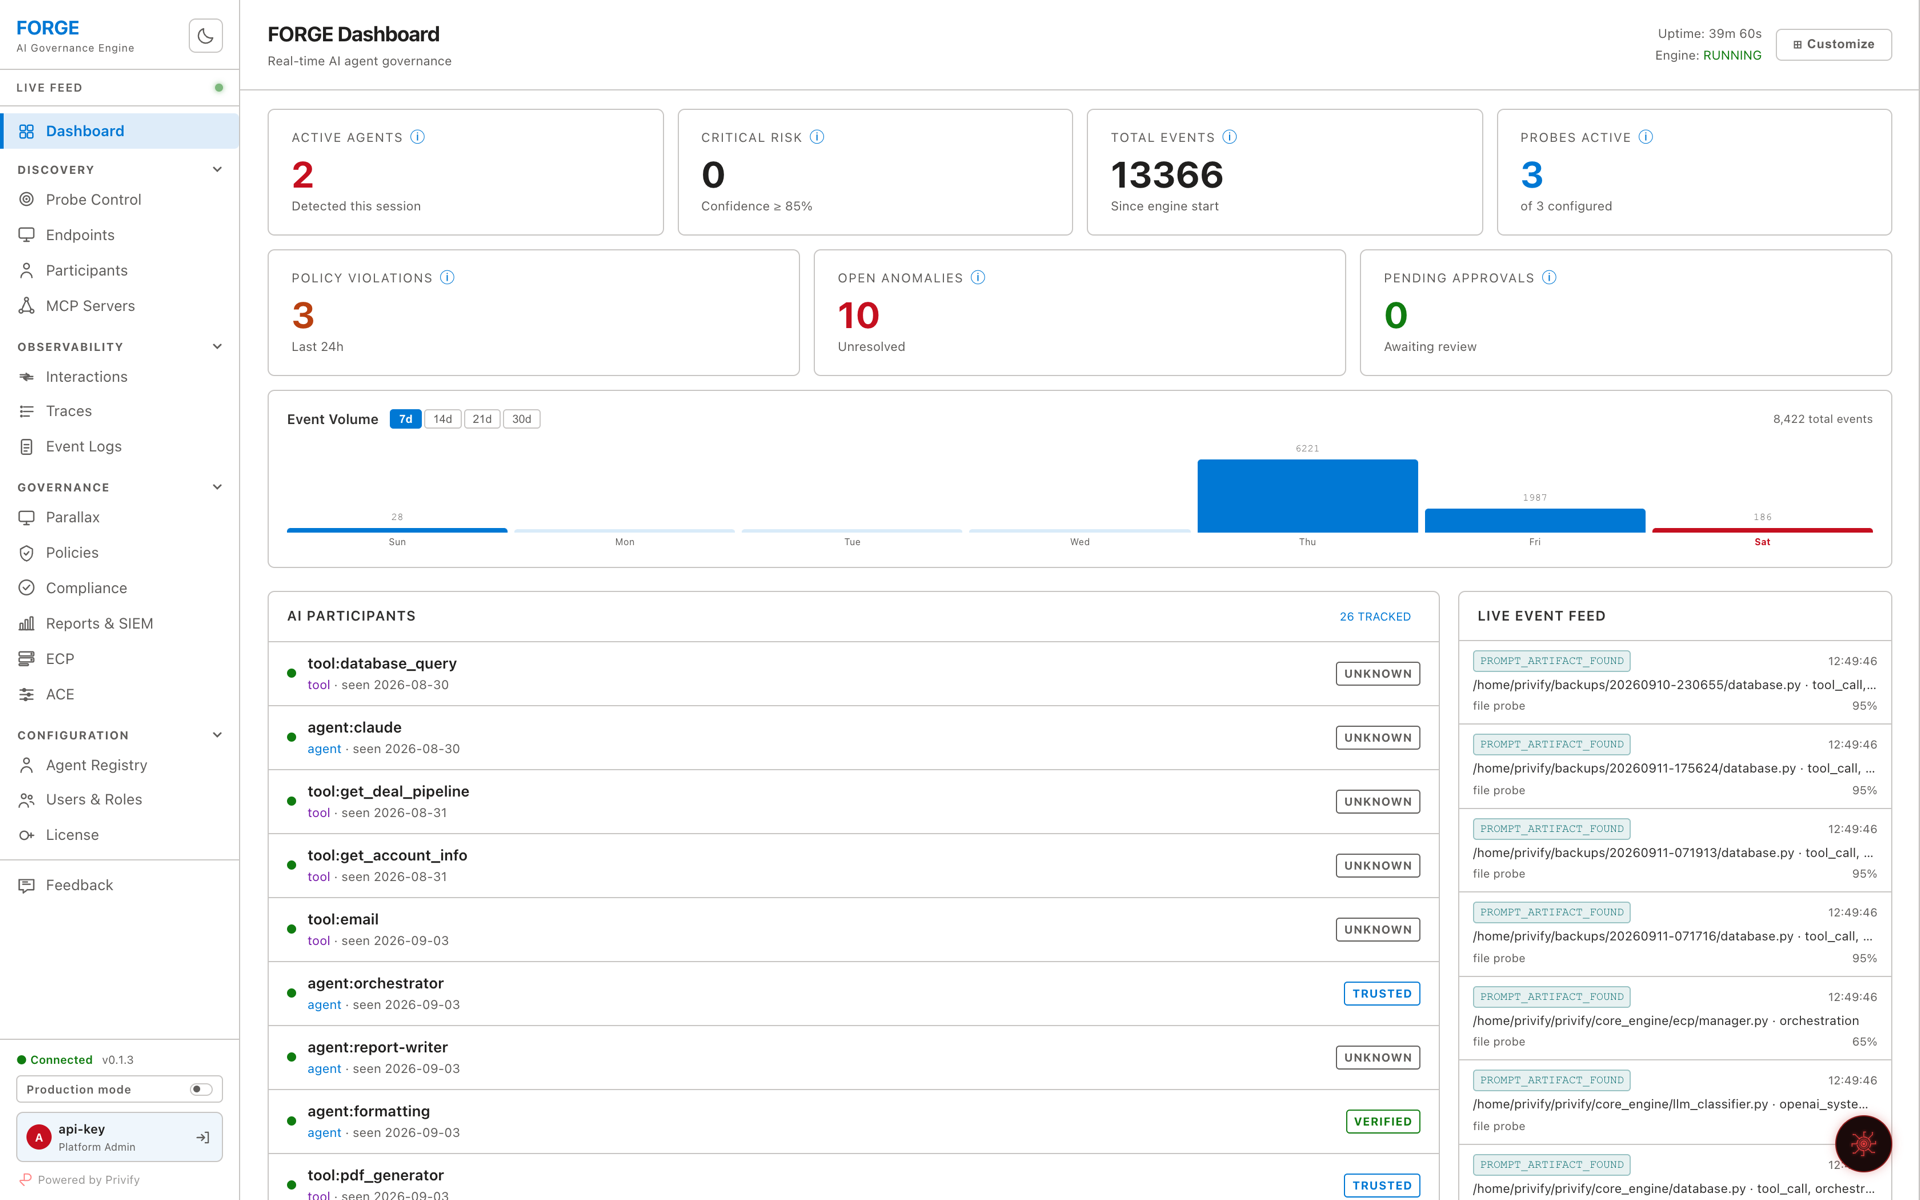
Not a mockup. This is the product.
Four panels, captured directly from a running deployment.
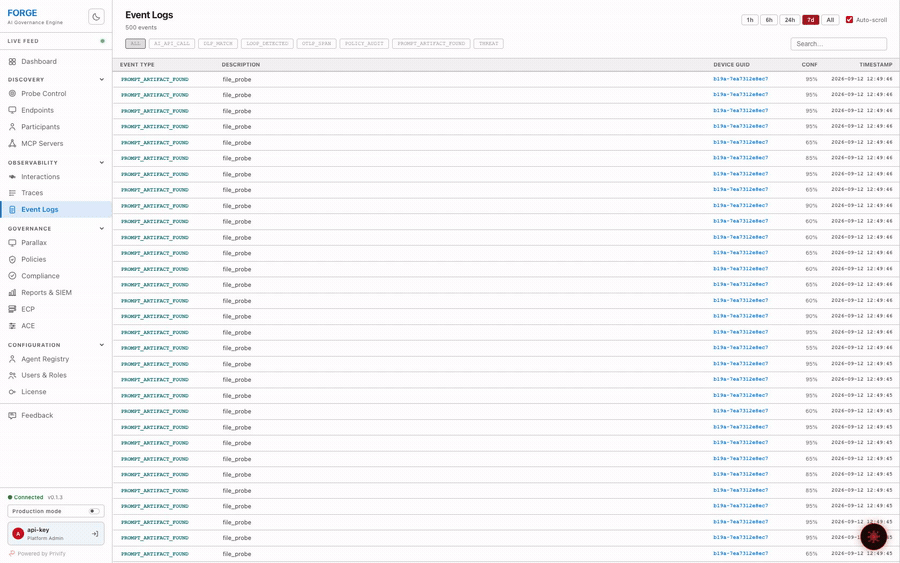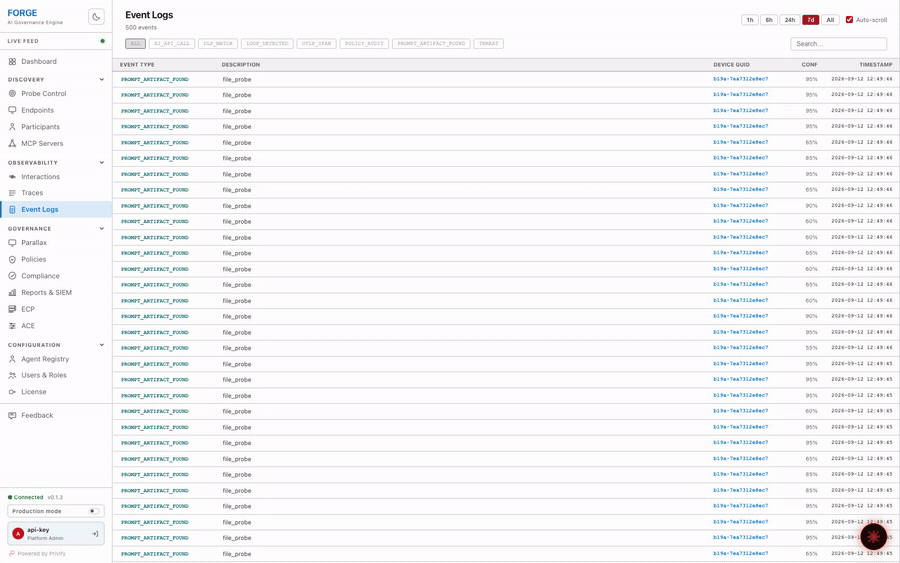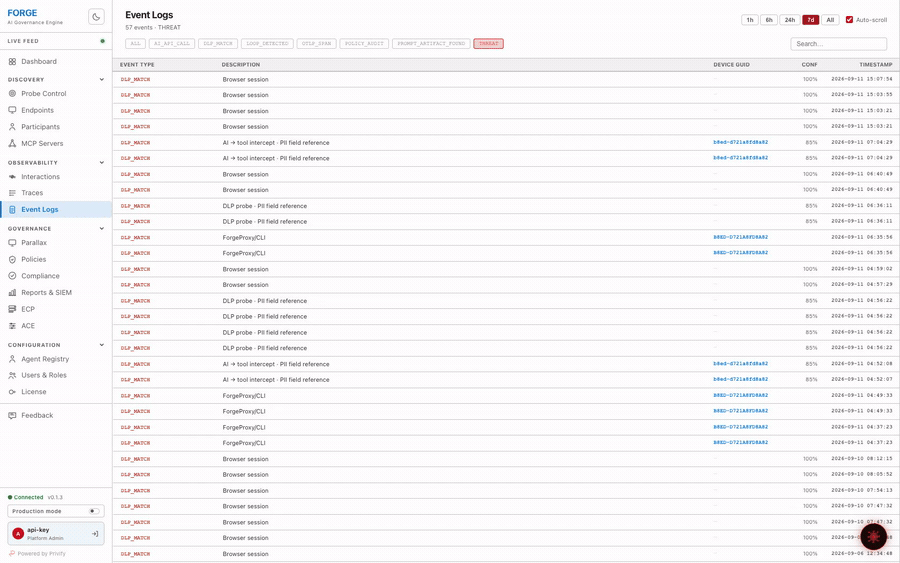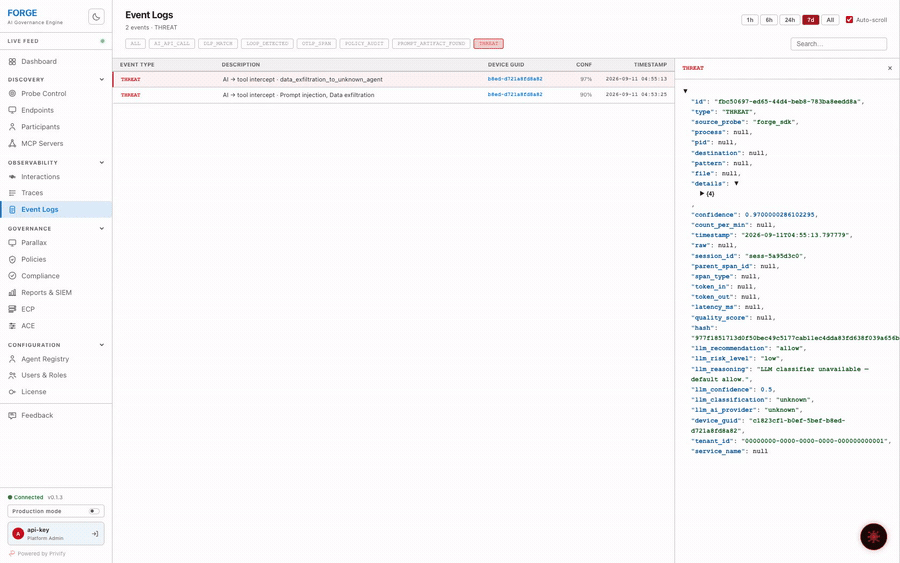
Platform that watches every surface an agent has
Browser sessions, the CLI proxy, tool calls, file probes — one event stream. Every match carries its confidence score and where it was caught, so a security review is a filter, not an investigation.
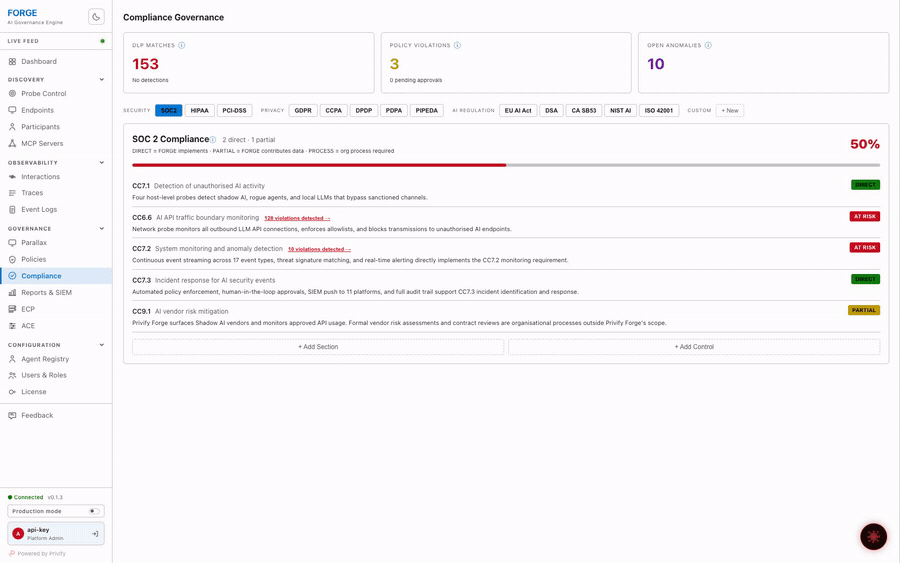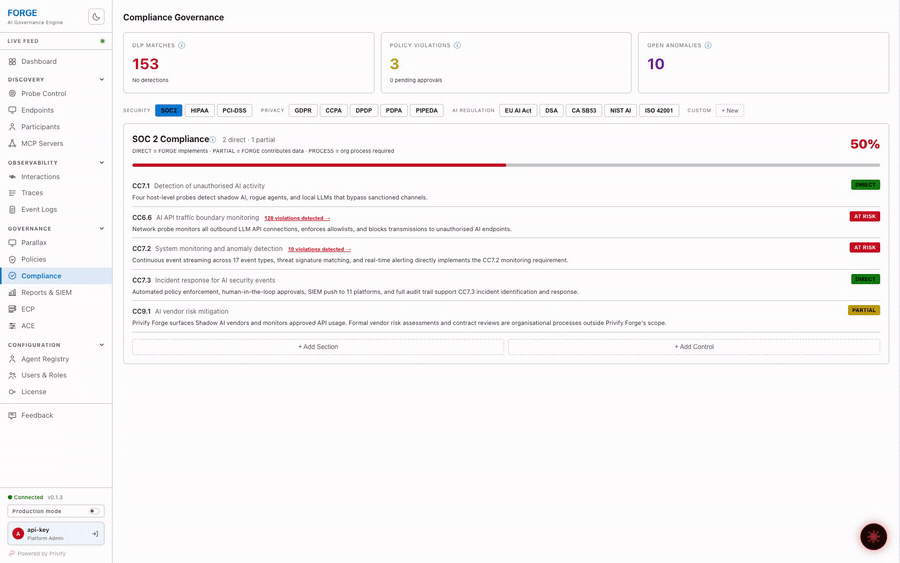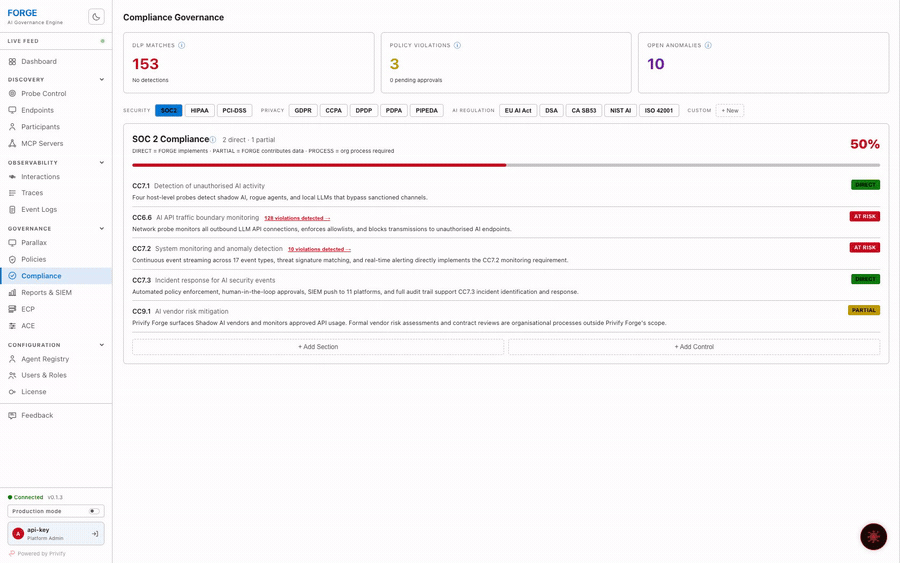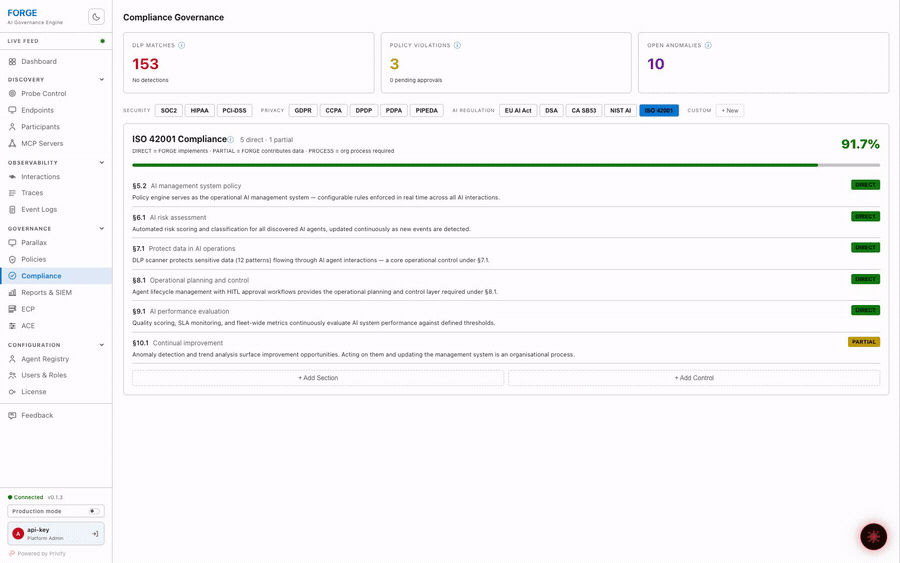
One event, mapped to every framework you report on
SOC 2, GDPR, HIPAA, the EU AI Act, ISO 42001 — switch frameworks and the same underlying evidence re-maps to the controls that framework actually asks for, article by article.
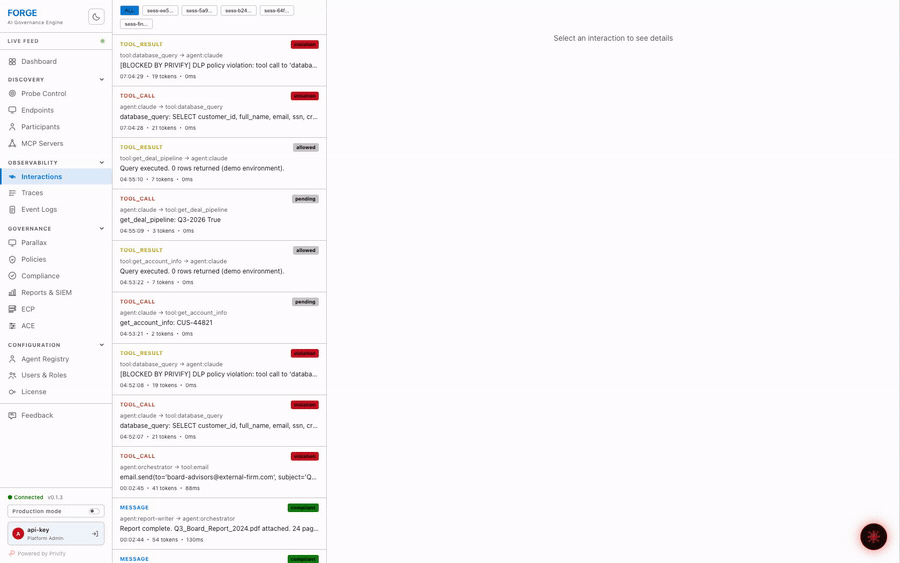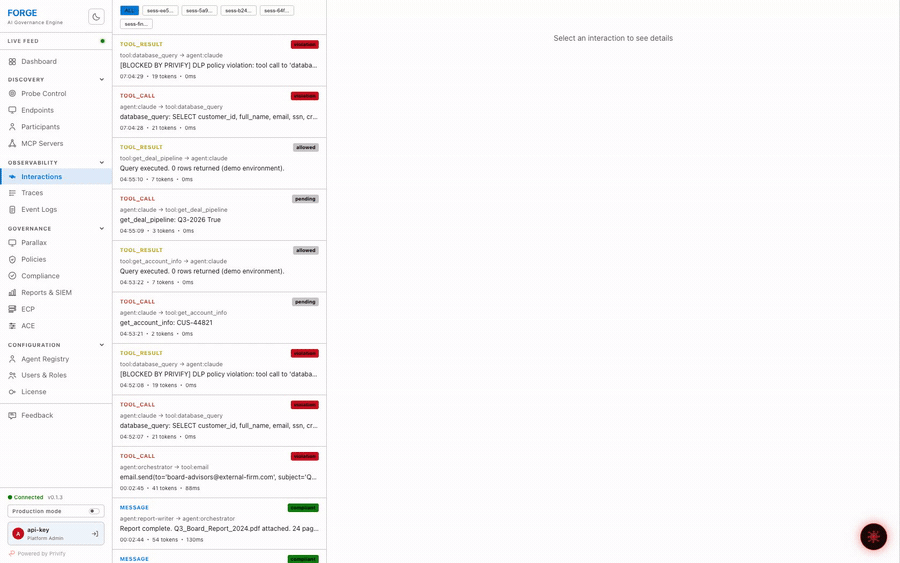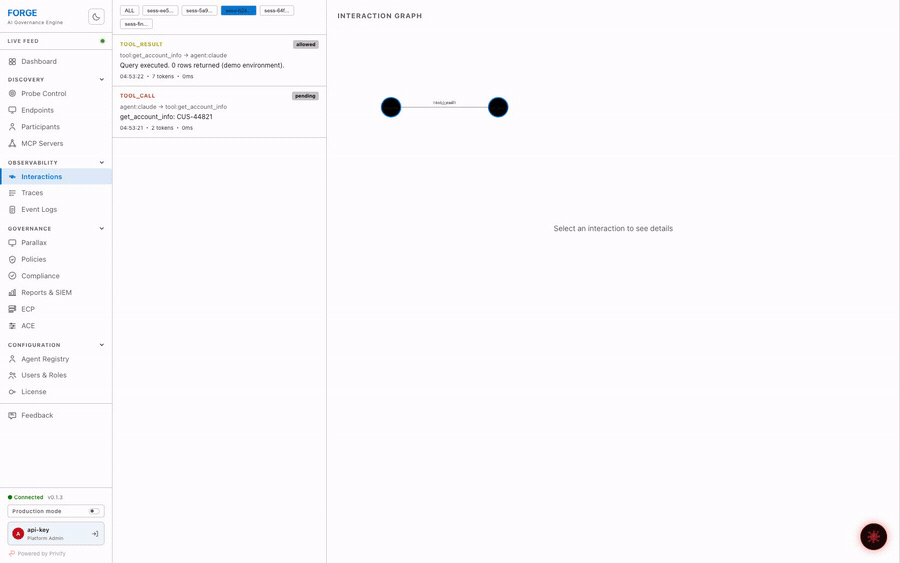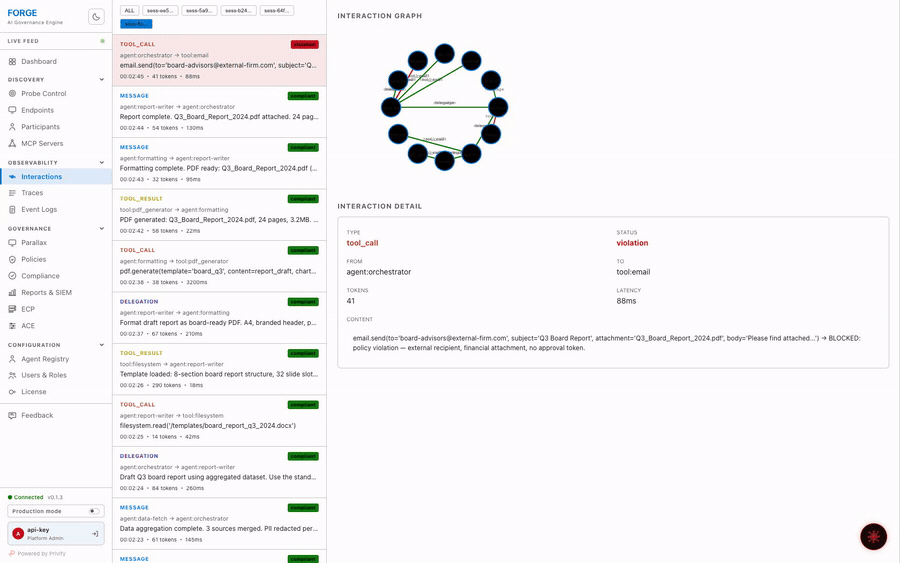
The full delegation chain, down to the step that got blocked
An orchestrator hands work to three other agents; one of them tries to email a board report to an external address. The graph shows the whole chain — and the detail pane shows exactly why that one step was refused.
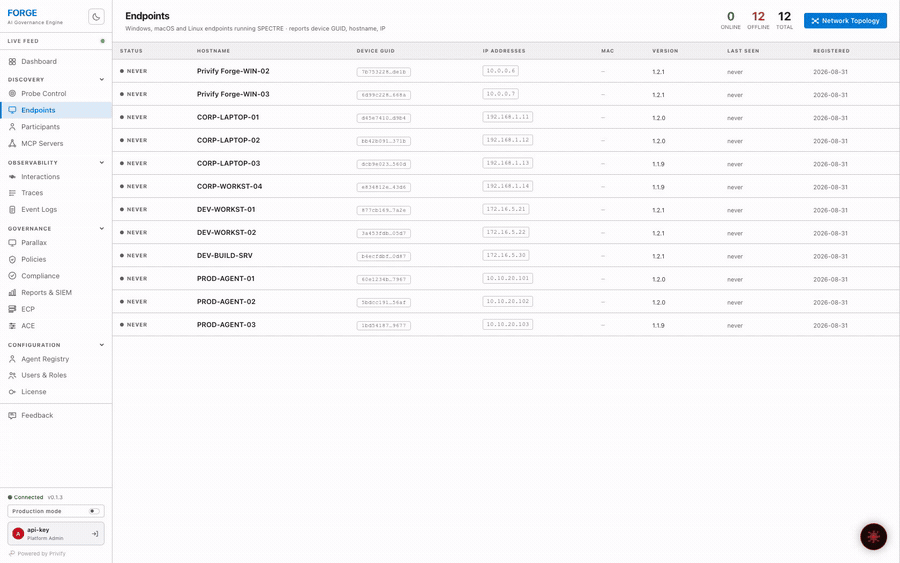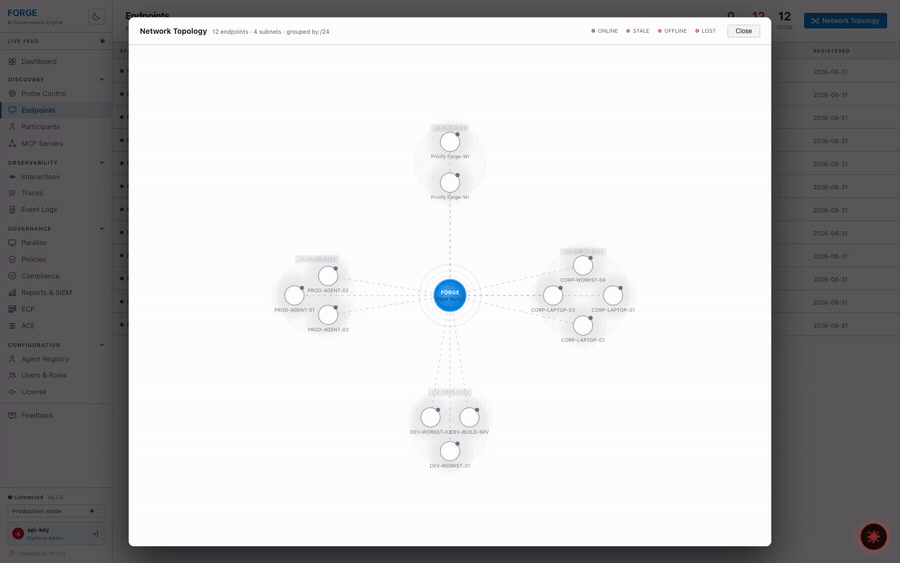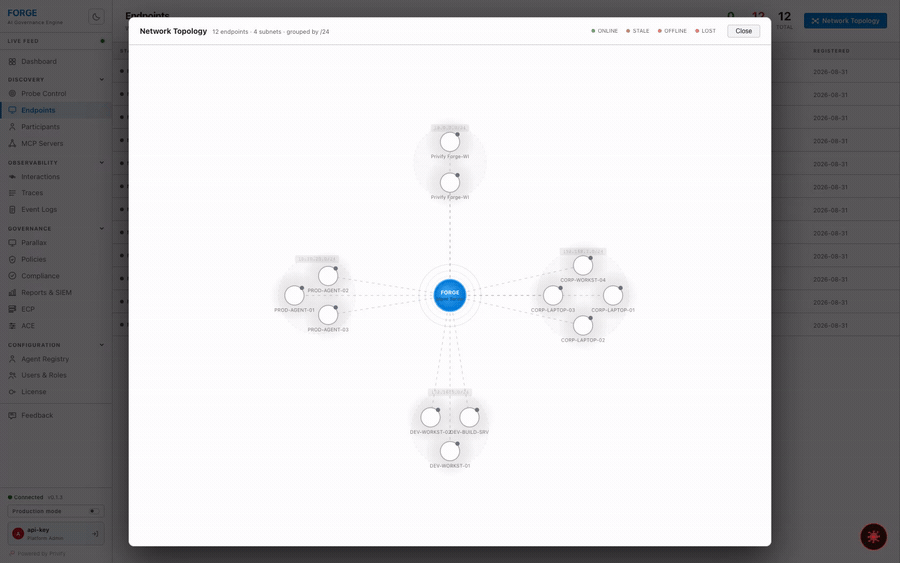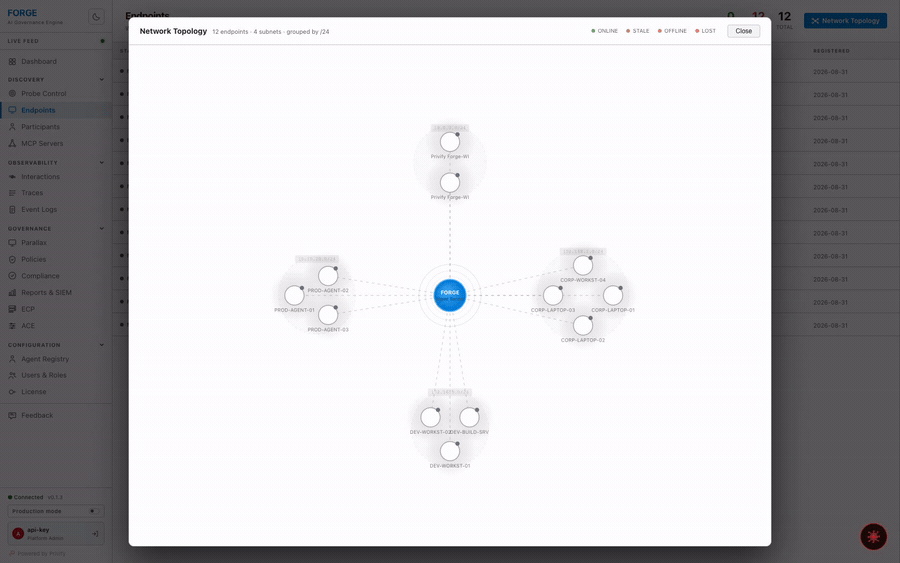
Every endpoint, grouped by the network it's actually on
No spreadsheet of hostnames — a live topology grouped by subnet, so "what's running in production" and "what's on someone's laptop" are visibly different questions.
Everything you need to govern AI at scale
Shadow AI detection
Discovers agents nobody registered — including local LLMs running on Ollama or LM Studio that generate zero outbound traffic. Process-level scanning, not proxy-level.
DiscoveryInteraction graph
Live SVG graph of every human→agent, agent→agent, and agent→tool interaction. Colour-coded by policy status. Click any edge for full context, token counts, and latency.
ObservabilityReal-time intervention
BLOCK, REDACT, FLAG, or PAUSE any interaction before the response reaches its destination. Policy evaluation runs on every message the moment it's captured.
GovernanceConfigurable DLP engine
Scans all interaction content for SSN, credit cards, API keys (OpenAI sk-*, AWS AKIA*), PHI, connection strings, and more — tune or extend detection to match your own data. Catches data in agent↔agent messages too.
SecurityAI firewall
Configurable threat signatures covering the OWASP LLM Top 10: prompt injection, jailbreak (DAN), system prompt extraction, data exfiltration, indirect injection via tools.
SecurityQuality SLAs
6-dimension quality scoring (relevance, accuracy, safety, compliance, helpfulness, hallucination risk) with per-agent thresholds and automatic ALERT or SUSPEND on breach.
GovernanceHuman-in-the-loop
Approval queue pauses policy-violating interactions. Reviewer sees full context — interaction graph, participants, risk score, matched policy — before approving or denying.
GovernanceCompliance reporting
19 frameworks: GDPR, HIPAA, SOC 2, PCI DSS, DPDP Act (India), PDPA (Singapore/Thailand), PIPEDA (Canada), EU AI Act, DSA, CA SB 53/AB 853, NIST AI RMF, ISO 42001, CCPA/CPRA, SR 11-7, NYDFS 500, GLBA, DORA, FINRA AI Guidance, Colorado AI Act. Tamper-evident SHA256 audit chain. CSV export.
ComplianceMeets you where your agents run
Six deployment components. Layer them for defense in depth. Start with one in five minutes. Scale to global enterprise without rearchitecting.
Single appliance or Docker
Network probe + HA appliance pair
All layers · global · per-region compliance
Admission webhook · zero config per pod
Built differently. Governed deeper.
Most governance tools sit at the network boundary. Privify reaches further — into the endpoint and into the delegation chain.
OS-level endpoint detection
Privify's endpoint probe scans running processes, detects AI library imports, and discovers local LLM servers (Ollama, LM Studio, vLLM) that generate zero outbound traffic. Network-only tools are completely blind to these. We aren't.
Unique capabilityFull interaction graph including agent↔agent
When Agent A delegates to Agent B who calls Tool C, we see and govern the entire chain. Most platforms only see the first hop — human sends prompt, AI responds. The real risk — data leakage, prompt injection, unauthorized delegation — lives in the delegation path.
Unique capabilityMid-flight intervention — not post-hoc alerting
Policy evaluation runs the moment an interaction is captured — before the response reaches its destination. BLOCK halts instantly. REDACT strips sensitive content and allows through. PAUSE suspends and opens a human approval queue. This is control, not just visibility.
Unique capabilityQuality SLAs linked to governance
Quality scoring (6 dimensions, every interaction) feeds directly into the governance engine. A quality SLA breach — hallucination rate exceeds threshold, task completion drops — triggers the same ALERT or SUSPEND workflow as a security policy violation. One control plane for both.
Unique capabilitySIEM-native, not SIEM-replacing
17 SIEM & security platforms supported across 5 export formats — CEF for Splunk, LEEF for QRadar, Syslog RFC 5424 for any receiver, ECS for Elastic, STIX 2.1 for threat intel platforms. Every event auto-forwards in real time. Your SOC team gets AI agent telemetry in the platform they already use.
Enterprise readyThe agents your gateway will never see
An MCP gateway governs what routes through it. That's real coverage — but an agent only routes through it when it chooses to speak MCP. Privify FORGE runs on the endpoint, where the agent actually executes.
Three kinds of AI activity, none of which pass through a protocol gateway. Privify FORGE catches all three because it runs where the code runs, not where the traffic is supposed to go.
Built for what others weren't
Most AI tools were built for a single persona — the engineer, the security team, or the compliance officer. Privify FORGE was designed from day one to serve all three, from a single deployment.
| Capability | Other platforms | Privify FORGE |
|---|---|---|
| Detection & Visibility | ||
| Shadow AI detection | Partial | OS + network + file system |
| Local LLM detection only Privify FORGE | Not available | Endpoint probe |
| Agent-to-agent visibility only Privify FORGE | Not available | Full interaction graph |
| Observability & Tracing | ||
| Trace DAG with replay | Basic or partial | Trace DAG with animated replay |
| MCP server governance | Not available | Autodiscovery |
| Security & Data Protection | ||
| DLP scanning | Limited or vendor-locked | Configurable engine · real-time |
| AI firewall & intervention | Guardrails only | 10 signatures · inline block |
| Human-in-the-loop approvals only Privify FORGE | Not available | Approval queue · configurable |
| Quality Governance | ||
| Quality SLAs | Partial — single dimension | 6 dimensions · enforced |
| Compliance & Integration | ||
| Compliance frameworks | 1–3 frameworks, basic | 19 frameworks · audit-ready |
| SIEM integration | Basic or single platform | 17 platforms · real-time forward |
| Deployment model | SaaS only or cloud-locked | Cloud · on-prem · airgap · hybrid |
platform offers
frameworks
integrations
all three personas
Fits into your existing stack
116 AI providers seeded. 17 SIEM platforms. Cloud discovery for AWS, GCP, and Azure. You don't rebuild your infrastructure — Privify slots into it.
AI providers
SIEM & Security
Cloud platforms
Observability & ITSM
Regulated differently. Governed accordingly.
Every regulated industry maps AI risk to a different set of controls. Privify FORGE ships with 19 frameworks pre-mapped to the configurable DLP engine and policy evidence — pick your industry to see which ones apply to you.
- 01 SR 11-7 treats an AI model the same as any other model — ongoing monitoring, documented outcomes, an inventory that actually stays current. Most banks can point to the first two and are guessing on the third.
- 02 Trading desks, underwriting, and customer support have all started running AI agents — usually before the model-risk team has a name for them, let alone a monitoring plan.
- 03 Privify FORGE closes that gap directly: SOC 2, PCI-DSS, SR 11-7 model-risk monitoring, NYDFS 500 anomaly detection, GLBA safeguards, and FINRA AI supervision controls all draw from the same real-time event stream, with an approval gate in front of anything that touches cardholder or account data.
- 04 Model-risk and compliance stop reconstructing what happened after the fact — the evidence was already being collected.
- 01 HIPAA doesn't distinguish between PHI leaked by human error and PHI leaked by an AI copilot summarizing a chart — the audit-control and breach-detection obligations are identical either way.
- 02 Clinical and care-ops teams have quietly adopted AI copilots for scheduling, summarization, and triage support — usually with no one from security in the loop.
- 03 Privify FORGE's DLP layer fingerprints PHI in agent traffic — MRN, date of birth, and other protected fields — and ties every match directly to a HIPAA audit-control requirement, not a generic alert.
- 04 Security gets exposure evidence they can hand an auditor, instead of reading agent transcripts by hand.
- 01 Enterprise customers now put "how do you govern your own AI use" in the security questionnaire — right next to SOC 2, and just as hard to fake.
- 02 Product and engineering teams are usually the fastest AI adopters inside a SaaS company — copilots, MCP servers, autonomous coding tools — often before security has a full list.
- 03 Privify FORGE discovers every agent and MCP server actually running across the fleet, sanctioned or shadow, and maps that coverage straight into SOC 2 and ISO 42001 controls.
- 04 The questionnaire answer becomes a report you export, not a claim you make.
- 01 The EU AI Act, Colorado's AI Act, and California SB 53 all share one demand underneath the different names: a documented risk assessment with evidence behind it, not a policy statement.
- 02 Agencies and large platforms are the first to feel each new rule land, usually with a real penalty attached if the evidence isn't there when it's asked for.
- 03 Privify FORGE maps agent activity directly to EU AI Act, NIST AI RMF, ISO 42001, California SB53, EU DSA, and Colorado's AI Act controls, off the same event trail used for every other framework.
- 04 One governance layer produces evidence for every jurisdiction you operate in, instead of one project per regulator.
- 01 GDPR, CCPA, India's DPDP, Singapore's PDPA, and Canada's PIPEDA each define processing, consent, and breach notification differently — and one AI conversation can cross all five without anyone noticing.
- 02 AI agents move customer data across borders by default, which is exactly the scenario none of these regimes were written assuming would happen this fast.
- 03 Privify FORGE tags PII by type the moment an agent touches it, and maps each match to GDPR, CCPA, DPDP, PDPA, and PIPEDA simultaneously — one DLP pass, five compliance mappings.
- 04 No separate compliance workstream per region your agents happen to touch.
Frameworks shown are ones Privify FORGE maps controls to today, across 19 total — GDPR, HIPAA, SOC 2, PCI DSS, DPDP, PDPA, PIPEDA, EU AI Act, DSA, CA SB 53/AB 853, NIST AI RMF, ISO 42001, CCPA/CPRA, SR 11-7, NYDFS 500, GLBA, DORA, FINRA AI Guidance, Colorado AI Act. Tamper-evident SHA256 audit chain on every event. CSV export for audit submission. Don't see a regime you need? Tell us — a new framework pack is usually the fastest thing we can add.
Running in minutes. Not months.
Start with zero infrastructure changes. Add layers as your needs grow. Each step delivers immediate value — independently.
Single container
Privify FORGE runs as a single Docker container. No database to configure, no agents to install, no proxy to route traffic through. Up and running in minutes.
DNS sinkhole
One config change to your internal DNS resolver. Instantly see every AI domain lookup from every device on your network — no agent install needed on any machine.
Endpoint agents
Deploy lightweight endpoint agents on developer machines and servers. Detects local LLMs, AI library imports, and filesystem artifacts — invisible to network-only tools.
SIEM integration
Connect your existing Splunk, Sentinel, or QRadar. All events forward automatically in CEF, LEEF, ECS, or STIX 2.1 — your SOC team sees AI telemetry immediately.
Where AI governance
is forged.
Every AI agent in your enterprise shaped, governed, and held to policy — the moment it acts.
Ready to govern your AI fleet?
We onboard enterprises in cohorts. Tell us about your environment and we’ll be in touch within 2 business days with a personalized demo and deployment plan.
Request accessNo spam. No sales calls without consent.